Audit Trial.
SaaS desktop app.
What does a scanner see? Into the head? Down into the heart?
Philip K. Dick.
This is Audit Trial, a compliance unified Audit Trail & Alerts Platform for Clinical Trial Ecosystem. I designed it end to end in 2025 at Science4Tech, for a pharma client running its own clinical trial infrastructure.

🚩️🚩️🚩️
1. CONTEXT.
Clinical trial operations rely on multiple interconnected applications (eCRF, CTMS, eTMF, RTSM, Data Hub). Each system generates critical audit data, but this information is typically fragmented, hard to monitor in real time, and difficult to analyze across applications.
Regulatory requirements (GxP, 21 CFR Part 11) demand complete traceability, timely detection of risk events, and controlled access, yet existing solutions often overwhelm users with raw logs while failing to surface what actually matters.
🔎️🔎️🔎️
2. PROBLEM.
The organization lacked a centralized, actionable audit trail capable of:
The organization lacked a centralized, actionable audit trail capable of:
- Providing a cross-application view of user activity
- Detecting critical or unusual behaviors early
- Supporting regulatory audits without manual data consolidation
- Demonstrating compliance with regulatory frameworks such as ISO/IEC 27001 and 21 CFR Part 11
- Audit logs were verbose but not insightful
- Alerts were either missing or too noisy
- Users struggled to understand why an event mattered
- Configuration of audit scope and retention was opaque
👂👂👂
3. SOLUTION.
We designed a unified Audit Trail & Alerts platform focused on clarity, compliance, and decision-making.
To balance regulatory depth with usability, the product was designed around two fundamental principles: event-first clarity and progressive disclosure. Rather than exposing raw system logs filled with technical identifiers and low-level metadata, the interface prioritizes meaningful, human-readable events that clearly communicate what happened, who performed the action, what was affected, and why it matters.
This ensures that QA, Security, and Study Managers can quickly understand activity across applications without deciphering technical noise. At the same time, the system preserves full traceability by layering information progressively. High-level dashboards provide situational awareness, the Activity Log offers structured event visibility, and detailed views expose complete compliance metadata only when needed. This approach reduces cognitive load in day-to-day operations while maintaining the depth required for regulatory audits and investigations.
🤸♀️🤸♀️🤸♀️
4. INFORMATION ARCHITECTURE.
The product was structured around four core areas:
The product was structured around four core areas:
- Dashboard — High-level situational awareness
- Alerts Inbox — Actionable alerts prioritized by severity, with clear context and direct links to underlying events
- Activity Log — A normalized, cross-application audit log with consistent event structure and advanced filtering
- Settings — Centralized alert configurations and governance controls

🪁🪁🪁
5. DESIGN PRINCIPLES.
- Event-first, not log-first — Users see meaningful events, not raw system noise.
- Severity is inherent, not subjective — Event severity is defined at the system level and reused consistently across logs and alerts.
- Progressive disclosure — High-level summaries first, technical metadata only when needed.
- Compliance by design — Actor identity, role-at-time, timestamps, and traceability are always preserved and visible. Roles change; the log remembers what you were when you did it.

🥼🧥🥼
6. OUTCOME.
The final product balances regulatory rigor with usability, transforming audit data from a passive compliance artifact into an active operational and risk-monitoring tool.
By unifying logs, alerts, and governance settings into a single, coherent experience, the platform enables teams to detect, understand, and act on critical events across the entire clinical trial ecosystem.


🛠️🛠️🛠️
7. RESULTS.
- became part of our client’s ISO/IEC 27001 certification process
- ⬇️ 35% reduction in time spent reviewing audit logs during QA checks
- ⚡ 60% faster detection of critical data integrity events
- 📉 40% fewer false-positive alerts thanks to clearer trigger definitions
- ✅ Improved audit readiness, with inspectors able to navigate events without assistance
Designer. Focus on product, UX & UI. Background in Art Direction and Motion Graphics. Sometimes I make books.
I was born in![]() on a 4th of July and some consequences had to remain, of course. In winter I like to use the
![]() . It is ugly. Indeed. But I can reach the 39 Celsius degrees that welcomed me into this world. And what a world.
![]()
![]()
![]()
![]() (I said Sanyo, is not a typo). Mortadella sandwiches with lemon Kas.
![]()
![]() (I said NASA, is not another typo). And screens with the same resolution. ALL. OF. THEM.
I especially like typeface, grids and things in movement. Some time ago I used to work on advertising.![]()
Someone who read this could think that Helvetica is such a boring choice for a typeface lover. And this person could be completely right on this point.
But this is not Helvetica :)
No, no. It is![]() Neue Haas Grotesk
I like it <3 Easy.
Speaking of something else, I like software. This can be weird, but is not false. I was from Figma when Adobe had not even heard of it and most of us were still using Sketch. I love Blender. Terrific piece of software and terrific project. I switched from Notion to Anytype. In Windows I use a very ugly font manager that I cannot recommend enough, despite its awful client service Maintype︎︎︎. In Mac I use RightFont. And of course, I took distance with Adobe and started using Affinity Serif. That being said, eternal respect for InDesign and its incredible baseline grid ❤️. And hate-love for AE.
In my spare time I do things like this︎︎︎ or this︎︎︎. Although I would like to do things like this︎︎︎, this︎︎︎ or this︎︎︎.
And that's all.
By now.
I was born in
Kansas City

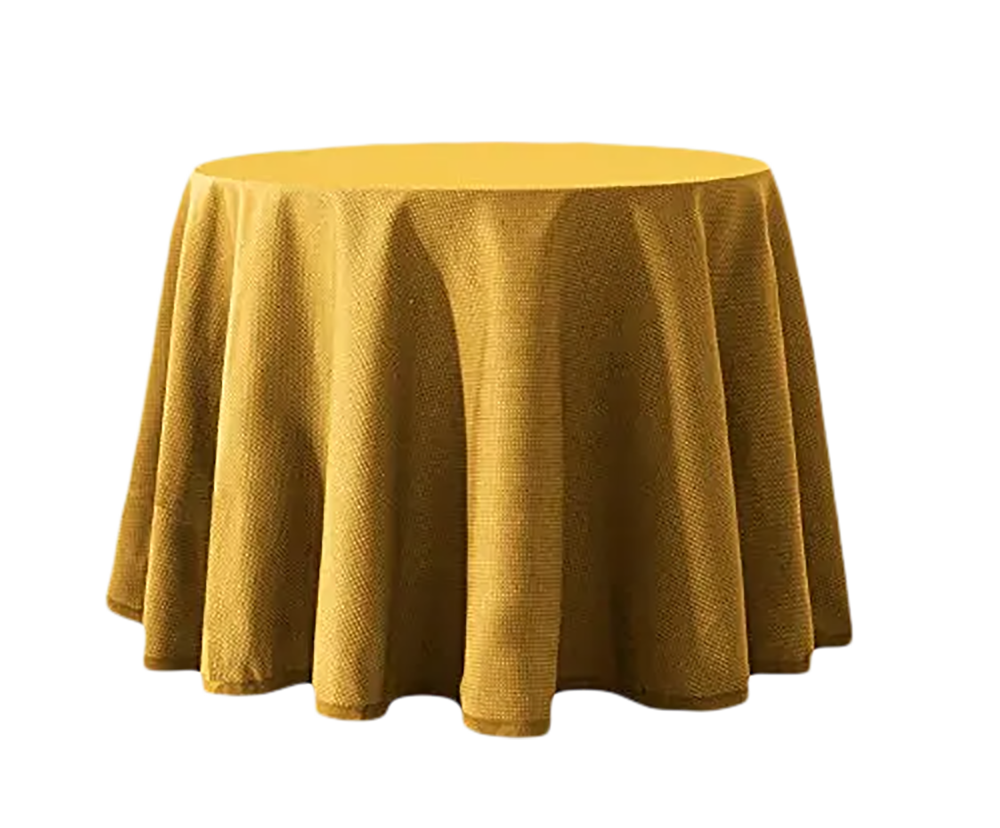
"mesa camilla"
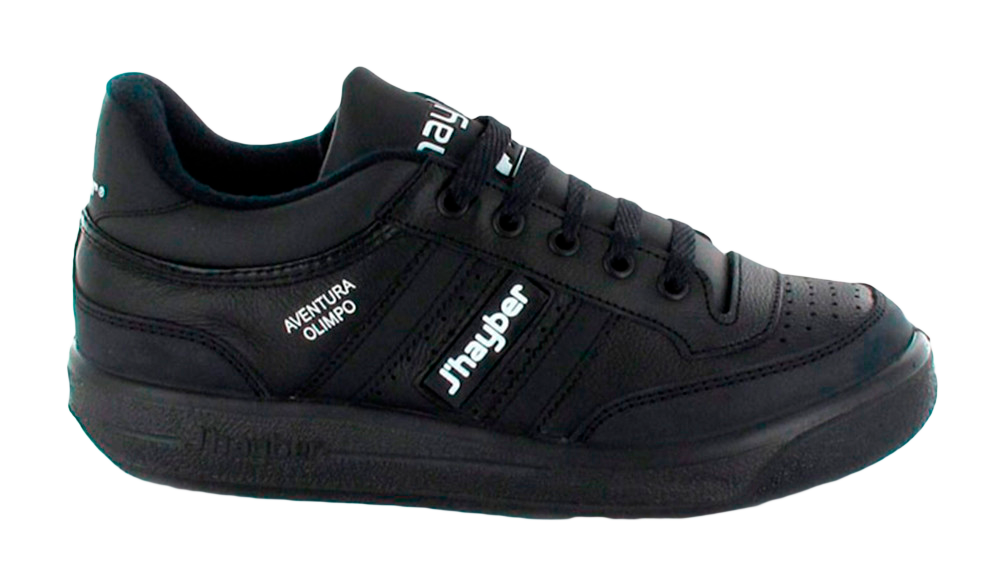
J'haybers,
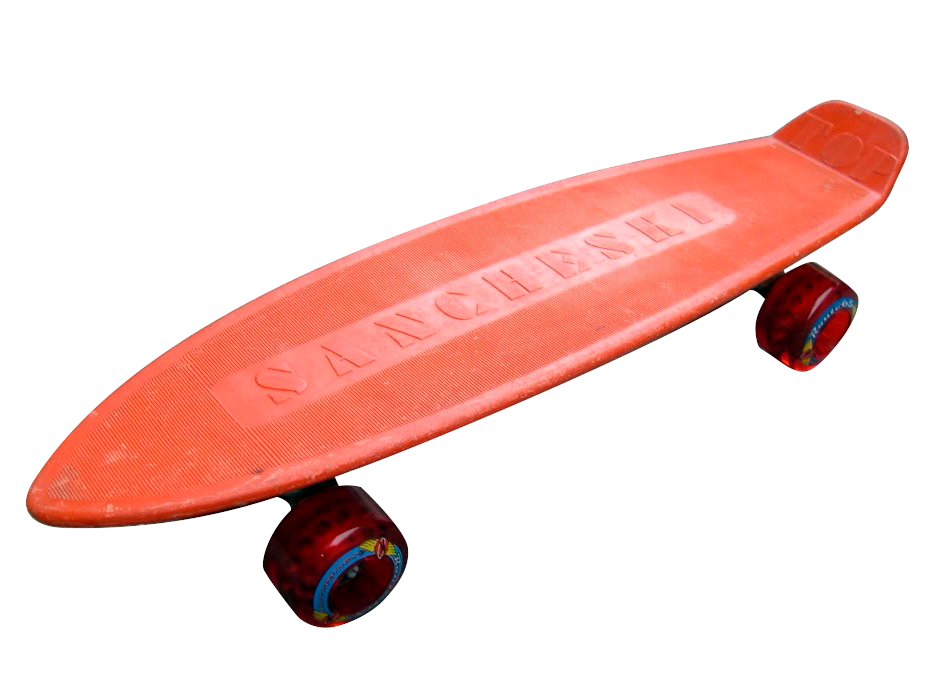
orange Sancheski,
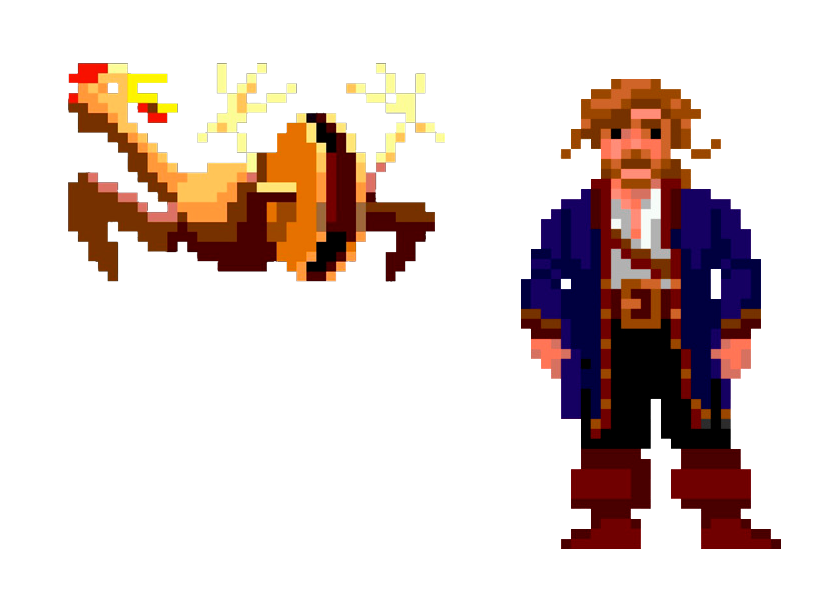
Monkey Island,
Sanyo with megabass
NASA
with Mario Bros
I especially like typeface, grids and things in movement. Some time ago I used to work on advertising.
It’s worse to beg.
Someone who read this could think that Helvetica is such a boring choice for a typeface lover. And this person could be completely right on this point.
But this is not Helvetica :)
No, no. It is
Christian Schwartz's

Speaking of something else, I like software. This can be weird, but is not false. I was from Figma when Adobe had not even heard of it and most of us were still using Sketch. I love Blender. Terrific piece of software and terrific project. I switched from Notion to Anytype. In Windows I use a very ugly font manager that I cannot recommend enough, despite its awful client service Maintype︎︎︎. In Mac I use RightFont. And of course, I took distance with Adobe and started using Affinity Serif. That being said, eternal respect for InDesign and its incredible baseline grid ❤️. And hate-love for AE.
In my spare time I do things like this︎︎︎ or this︎︎︎. Although I would like to do things like this︎︎︎, this︎︎︎ or this︎︎︎.
And that's all.
By now.
